

Intelligence Hub
Explore the latest research, advisories, insights, and events in our Intelligence Hub.

CVE-2025-13032: Entering and Breaking the Avast Antivirus Sandbox Part 2
This post is the second and final part of our Avast Antivirus research, detailing the full exploitation of CVE-2025-13032 on an up-to-date Windows 11 system. Starting from the double-fetch vulnerability introduced in Part 1, we walk through how the controlled paged pool overflow was turned into an arbitrary kernel read/write primitive by corrupting the RegBuffers array of the IORing object. The post covers the heap spray strategy, the kernel address leak via MDL introspection, the repairs needed to avoid a blue screen on teardown, and the final privilege escalation to SYSTEM via token theft.


CVE-2025-13032: Entering and Breaking the Avast Antivirus Sandbox Part 1
SAFA discovered four distinct kernel heap overflow vulnerabilities in Avast Antivirus. Our research targeted the aswSnx kernel driver, first requiring interesting sandbox manipulation to reach the attack surface. CVE-2025-13032 was assigned to these patched vulnerabilities. This first blog post introduces the vulnerabilities and the challenges of the custom sandbox profile. While a consecutive post will detail how the primitive was exploited for Local Privilege Escalation to System.
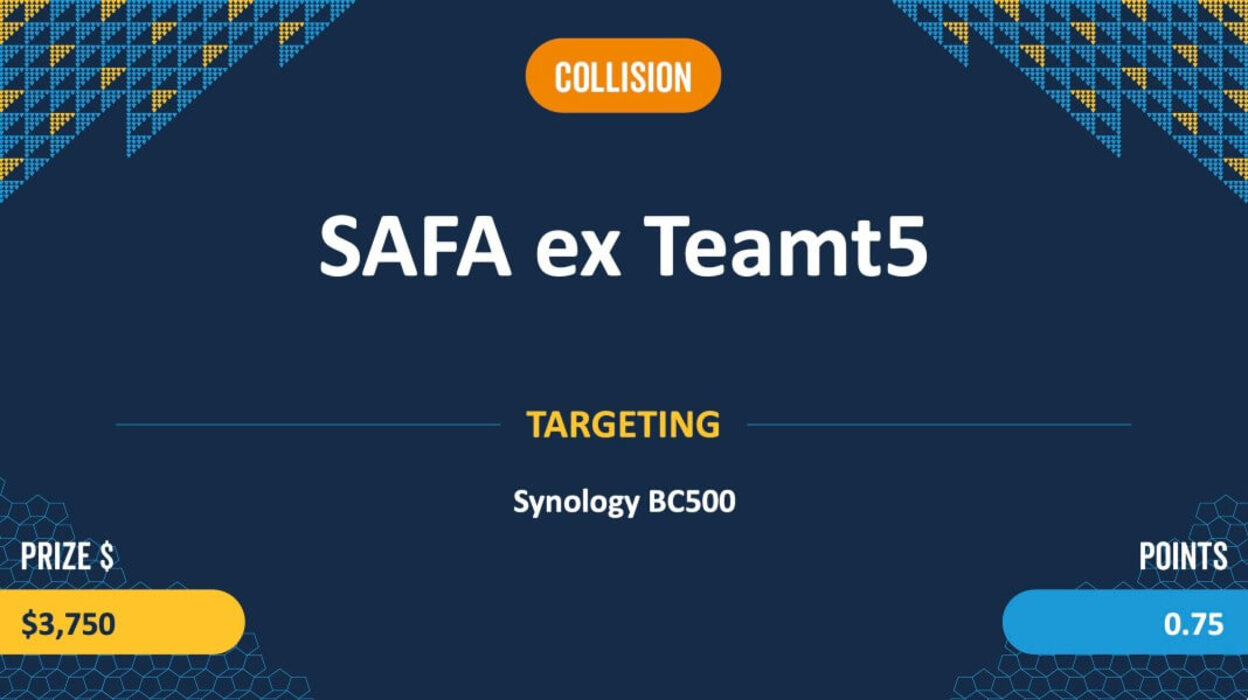
SAFA & TeamT5 at Pwn2Own: Vulnerability Demonstration Insights
Cybersecurity is always a work in progress. That’s why SAFA and our key partner, TeamT5, regularly participate in ethical hacking events. They provide a venue to learn about current real-world security issues and sharpen our skills in solving them. This is why we traveled to Toronto, Canada, for the most recent Pwn2Own competition.
Talk to us about your threat intelligence needs
Tell us what you're defending and we'll show you how ThreatVision fits.